Live terminals
Full xterm sessions over WebSocket with scrollback replay. Reconnect from anywhere. The PTY keeps running on the server.
Self-hosted · single binary · your metal
helvi.sh is a self-hosted web SSH client and desktop for your server fleet. Open a browser and you get windows: shared terminals, host-to-host SFTP, monitors, containers and systemd. Folder grants decide who can open what. It ships as one Go binary with an embedded UI and a single SQLite file. The hosts only need SSH. No SaaS in the middle.
curl -fsSL https://get.helvi.sh | sudo bash
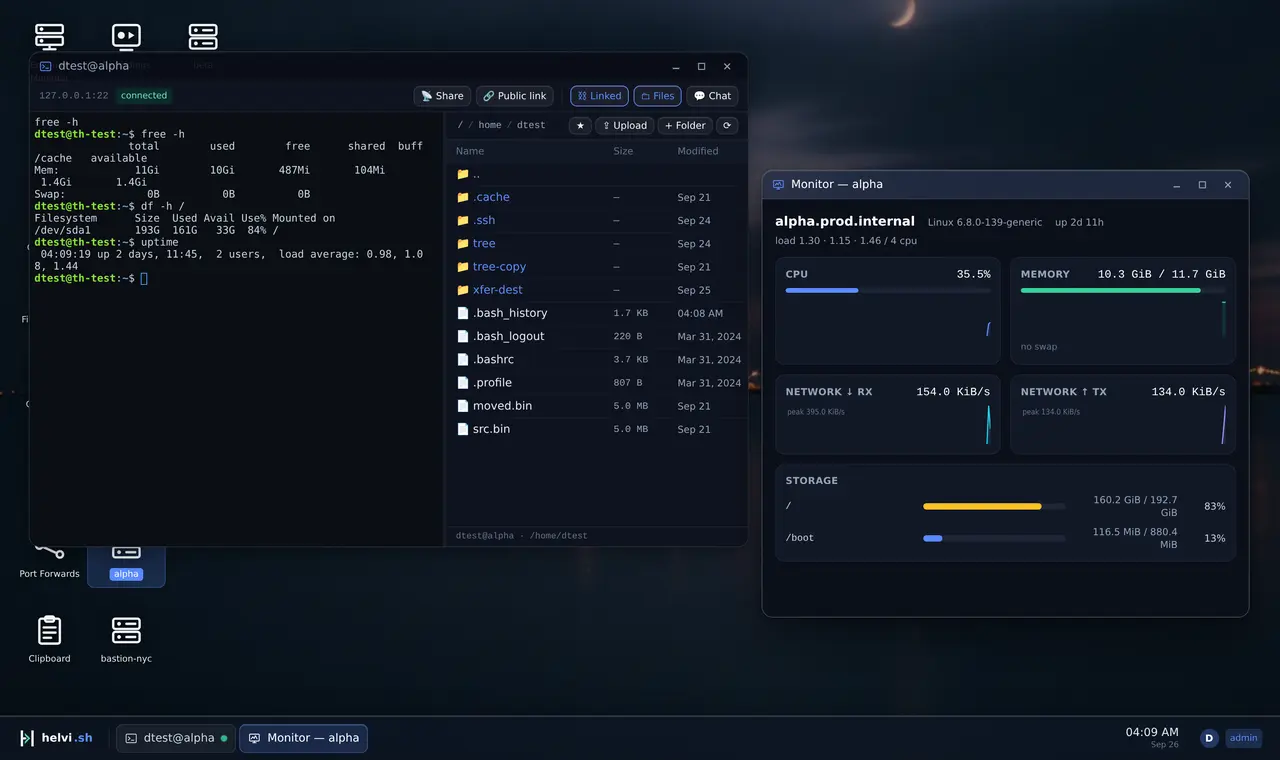
Windows you drag, resize, minimize and restore, with a taskbar, nested folders, a trash can and wallpapers. Ctrl+K searches every endpoint, app and playbook. Your layout is saved per user and restored on sign-in.
helvi.sh talks plain SSH and SFTP to your endpoints. If you can ssh to it, you can manage it: no agents required, no firewall gymnastics. Want metric history? A one-file daemon is there when you opt in.
SSH keys stay in the encrypted vault. Shell recording is on unless you turn it off. The audit log gets logins, sessions, transfers and admin actions. Admins are not bound by folder grants. Members are.
Every tool opens as a window on the same desktop, against the same endpoints, under the same permissions.
Full xterm sessions over WebSocket with scrollback replay. Reconnect from anywhere. The PTY keeps running on the server.
Browse two endpoints side by side and drag files across. Host-to-host transfers stream server-side through a queued SFTP pipeline. A search box digs through remote trees by name.
Live CPU, memory, network and storage sparklines per host, streamed over the same SSH connection. No exporters to deploy.
Docker containers and systemd units, in their own windows: status, logs, restart.
One-shot commands and saved playbooks fanned out across many hosts at once, with per-host output collected as it lands.
SSH tunnels from a window: open a listener on the helvi host through any endpoint, and close it there.
Shells record as gzipped asciicast v2 on disk. SQLite keeps the index, not the cast. Replay in the built-in player. It stores terminal output, not keystrokes.
SSH keys and agent credentials are sealed with age (X25519) under a key that never leaves your box. Write-only from the API.
Members only get the folders you grant, and only connect, read files, or write files on that grant.
TOTP apps, email or SMS codes, backup codes, all optional or enforced org-wide. Plus a PIN lock screen with auto-lock on idle.
Sign-ins, connections, transfers, admin changes, every agent command: timestamped, attributed, queryable from the Audit window.
Pin Grafana, your NAS, an internal wiki, or any other http(s) panel as sandboxed desktop windows next to your terminals.
Pin CPU, memory, disk and network cards straight onto the wallpaper. History comes from a tiny opt-in daemon on each host, stored in your database with retention you set.
Nest endpoints and playbooks in folders; permissions follow the tree down. Deletes go to a trash with a retention window, so a fat-fingered right-click isn't a disaster.
Export any endpoint or folder as a .helvi file. Credentials stay in the vault, never in the file. Optionally passphrase-encrypt it, then a teammate drags it onto their desktop to import.
Open a node's Proxmox web GUI in one click. helvi mints a short-lived, least-privilege account per person. The root password is never shared and every action has a name on it.
Share a live session with a teammate and both of you see the same terminal, byte for byte. One person types at a time. Control passes with an explicit hand-off, so there's never two cursors fighting over one shell.
Need eyes from outside? Mint a public view-only link: watchers see output in real time but can't type, can't browse, and the link dies the moment you revoke it or the session ends.
maria joined the session (view)
dtest@alpha:~$ journalctl -u api --since -5m | tail -3
Sep 26 04:02:11 alpha api[912]: timeout dialing 10.0.4.7:5432
Sep 26 04:02:14 alpha api[912]: retry 1/5 …
control handed to maria
maria@alpha:~$ pg_isready -h 10.0.4.7
10.0.4.7:5432 - accepting connectionsAttach a Claude-powered agent to any live session from its chat panel. It works through the same PTY you're watching: every command it runs is echoed in the terminal with a visible agent banner, captured in the recording, and written to the audit log.
The agent runs in a container on your helvi server, reaches the endpoint only through the session it's attached to, and its credentials are sealed in the vault. The agent never holds an SSH key. helvi does.
you › disk is filling up on this box, find the culprit
◆ agent du -x -d2 /var 2>/dev/null | sort -rn | head -3
9812340   /var/log/journal
1240310   /var/lib/docker
 812200   /var/cache/apt
agent › journald is 9.4 GB. Cap it with
SystemMaxUse=1G in journald.conf?The team reaches hosts through helvi.sh. Accounts, keys and the audit log are the part you have to get right.
Local accounts with argon2id hashing, or single sign-on against any OIDC provider (Okta, Entra, Keycloak, Google). Sessions are opaque and server-side, never JWTs in localStorage.
Authenticator apps (TOTP), email and SMS codes, single-use backup codes. Make 2FA optional, required for admins, or required for everyone. Enforcement happens before the desktop loads.
Grants are (user or group) × endpoint folder × capability: connect, read files, write files. If it isn't granted, the API returns 403.
Private keys and agent credentials are envelope-encrypted with age (X25519) under a boot-sealed master key. The first-run wizard makes you back it up, then never shows it again.
Session recordings plus an append-style audit log: who signed in, who connected where, who moved which file, what every agent executed. Attribution survives shared sessions.
One static binary, one SQLite file, no runtime dependencies to patch. Ship it behind Caddy or Traefik, health-check /healthz, done.
One Linux box is all it takes. Your data never leaves it.
curl -fsSL https://get.helvi.sh | sudo bashInstalls Docker if missing (it asks first), generates the vault passphrase into root-only /etc/helvi/helvi.env, and starts the container. Idempotent: rerun the same command any time to upgrade; your data and settings survive.
docker run -d --name helvi --restart unless-stopped \
  -p 8080:8080 -v helvi-data:/var/lib/helvi \
keoir/helvi-shA ~30 MB Alpine image running as non-root. Everything (database, vault, recordings) lives in the /var/lib/helvi volume. Front it with Caddy or Traefik for TLS.
make all                          # embedded UI + static binary → bin/helvi
sudo cp bin/helvi /usr/local/bin/
sudo systemctl enable --now helvi # unit file ships in deploy/Go ≥ 1.23 and Node ≥ 18 build the whole thing. The result is a single static binary (CGO-free, SQLite embedded) that runs anywhere Linux does.
curl -fsSL https://get.helvi.sh | sudo bash